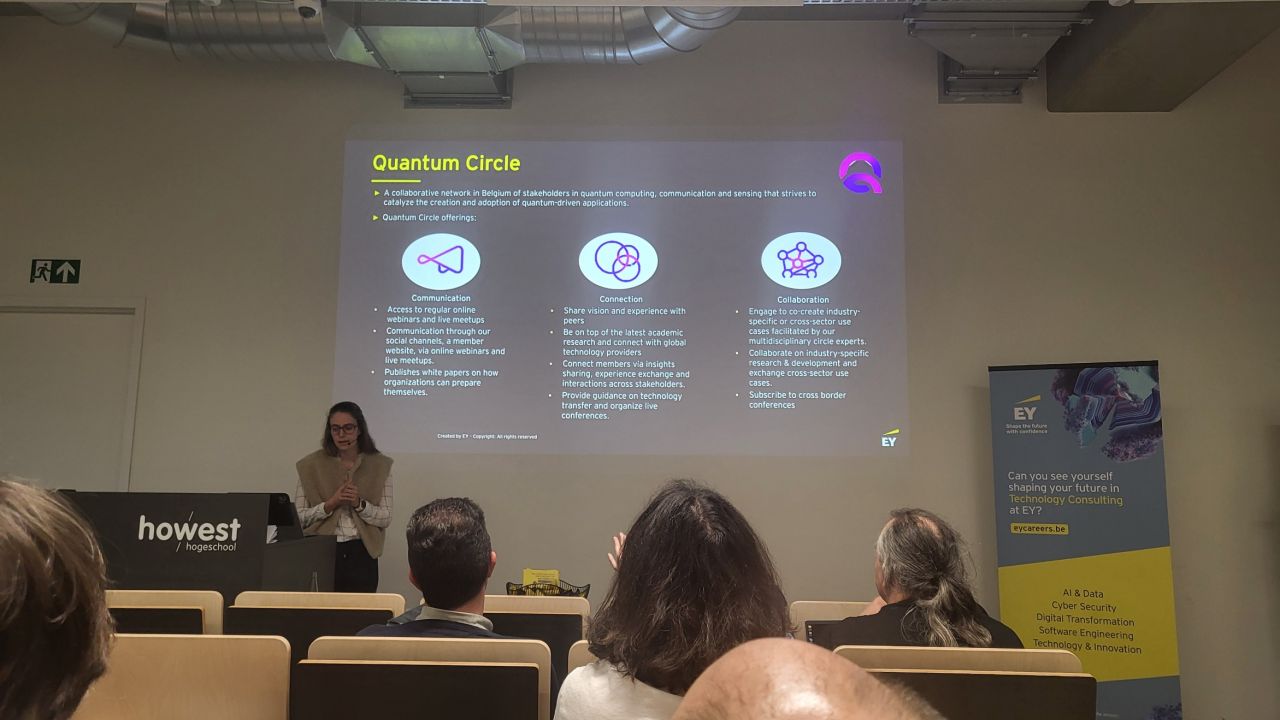
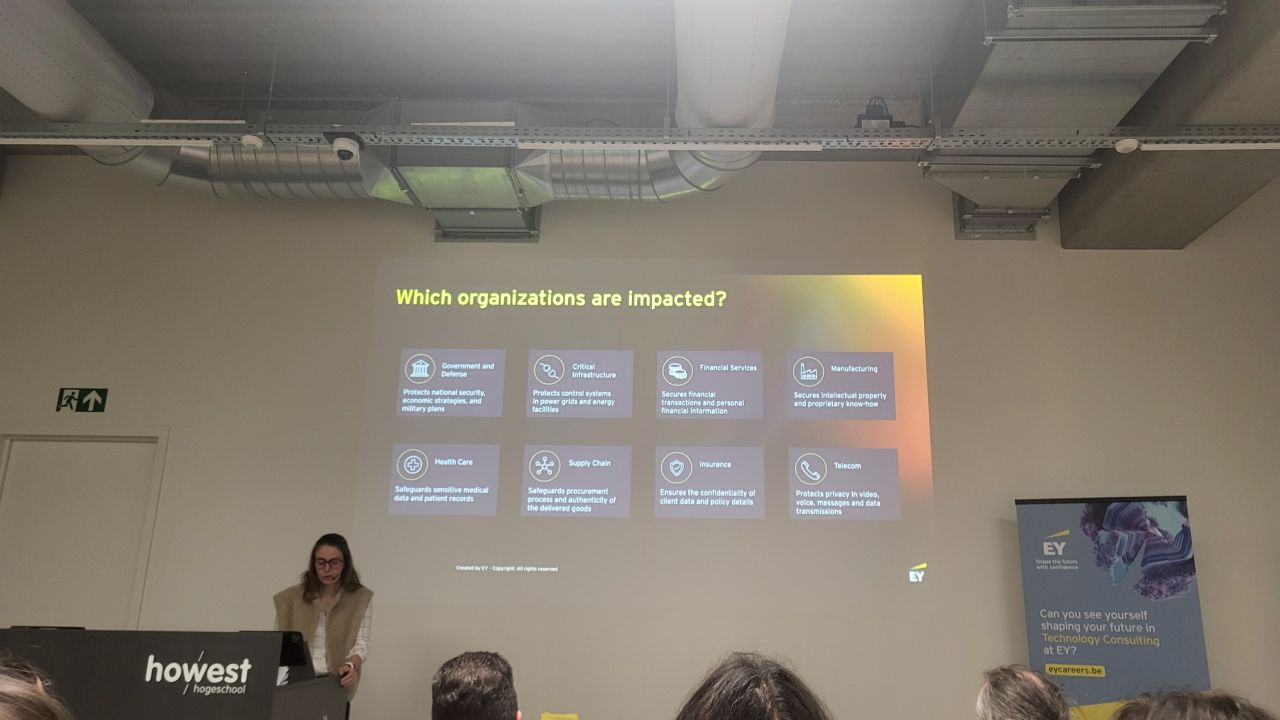
Last week I attended a Tech & Meet session hosted by HOWEST University of Applied Sciences regarding Post-Quantum Cryptography (PQC) by Sarah Ampe. It was a deep dive into a field that is rapidly moving from theoretical research to a critical requirement for modern software architecture.
Here are five key insights I gathered from the session:
The nature of Qubits: A fundamental shift in understanding is that qubits represent a probability rather than a simple binary state. This allows computing power to rise exponentially with the number of qubits, creating a scale of processing power that classical computers simply cannot match.
A Hybrid Future: Quantum computing is not a universal replacement for traditional computing. Both have distinct advantages; classical systems will continue to handle standard logic and tasks, while quantum will be reserved for specific, complex problem sets.
The Progress of PQC: Research into post-quantum algorithms has been intensive since at least 2016. We are now seeing the first of these algorithms become standardized, marking the beginning of a major transition in global security protocols.
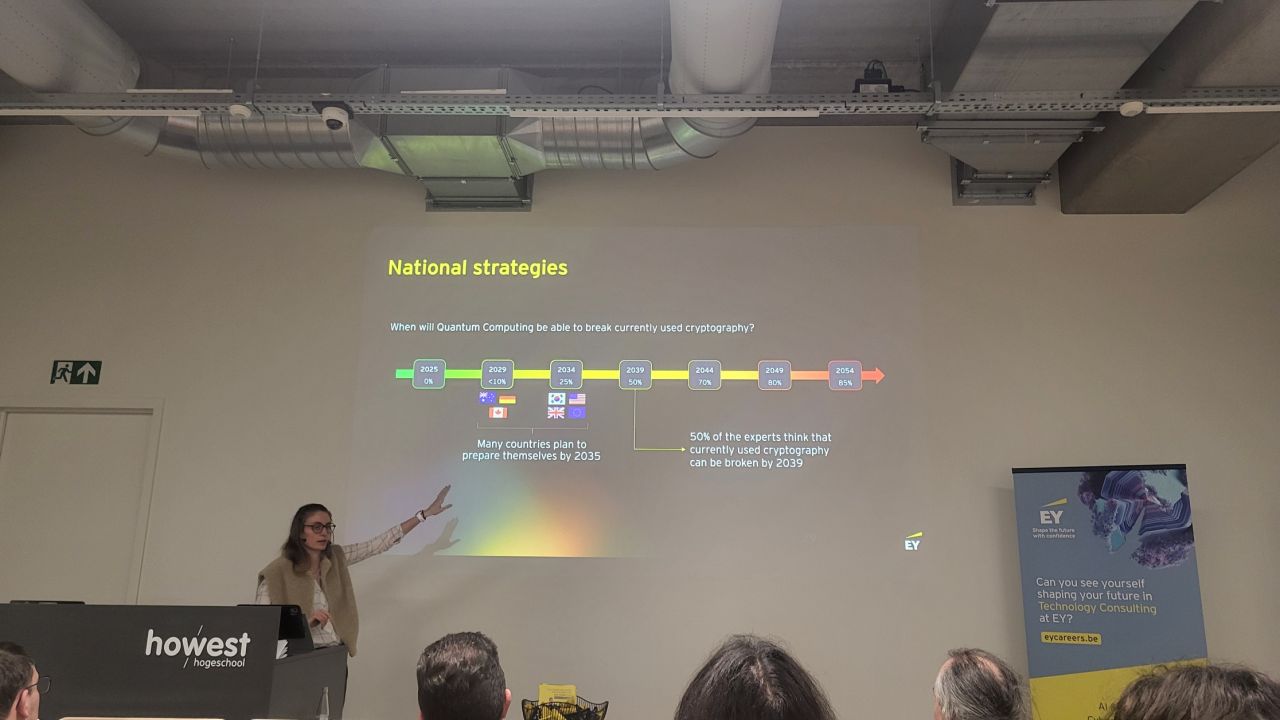
The 2039 Benchmark: While the threat is real, the hardware is still maturing. According to expert consensus, there is roughly a 50% chance that public-scale quantum computers will be a reality by 2039.
The Concept of Data Longevity: This was perhaps the most vital takeaway. Different types of data have different "shelf lives" — some must remain secure for 10, 15, or even 50 years. If your data needs to remain secret for 15 years, but a quantum computer arrives in 10, that data is already at risk today.
The session reinforced that "Quantum Readiness" isn't just about future hardware; it's about the cryptographic choices we make in our development pipelines today.
Many thanks to Sarah Ampe for providing such a clear explanation for what is often a very abstract topic.